Opis
Crack the DevSecOps interviews
KEY FEATURES
Master DevSecOps for job interviews and leadership roles, covering all essential aspects in a conversational style.
Understand DevSecOps methods, tools, and culture for various business roles to meet growing demand.
Each chapter sets goals and answers questions, guiding you through resources at the end for further exploration.
DESCRIPTION
DevOps took shape after the rapid evolution of agile methodologies and tools for managing different aspects of software development and IT operations. This resulted in a cultural shift and quick adoption of new methodologies and tools.
Start with the core principles of integrating security throughout software development lifecycles. Dive deep into application security, tackling vulnerabilities, and tools like JWT and OAuth. Subjugate multi-cloud infrastructure with DevSecOps on AWS, GCP, and Azure. Secure containerized applications by understanding vulnerabilities, patching, and best practices for Docker and Kubernetes. Automate and integrate your security with powerful tools. The book aims to provide a range of use cases, practical tips, and answers to a comprehensive list of 150+ questions drawn from software team war rooms and interview sessions.
After reading the book, you can confidently respond to questions on DevSecOps in interviews and work in a DevSecOps team effectively.
WHAT YOU WILL LEARN
Seamlessly integrate security into your software development lifecycle.
Address vulnerabilities and explore mitigation strategies.
Master DevSecOps on AWS, GCP, and Azure, ensuring safety across cloud platforms.
Learn about patching techniques and best practices for Docker and Kubernetes.
Use powerful tools to centralize and streamline security management, boosting efficiency.
WHO THIS BOOK IS FOR
This book is tailored for DevOps engineers, project managers, product managers, system implementation engineers, release managers, software developers, and system architects.
TABLE OF CONTENTS
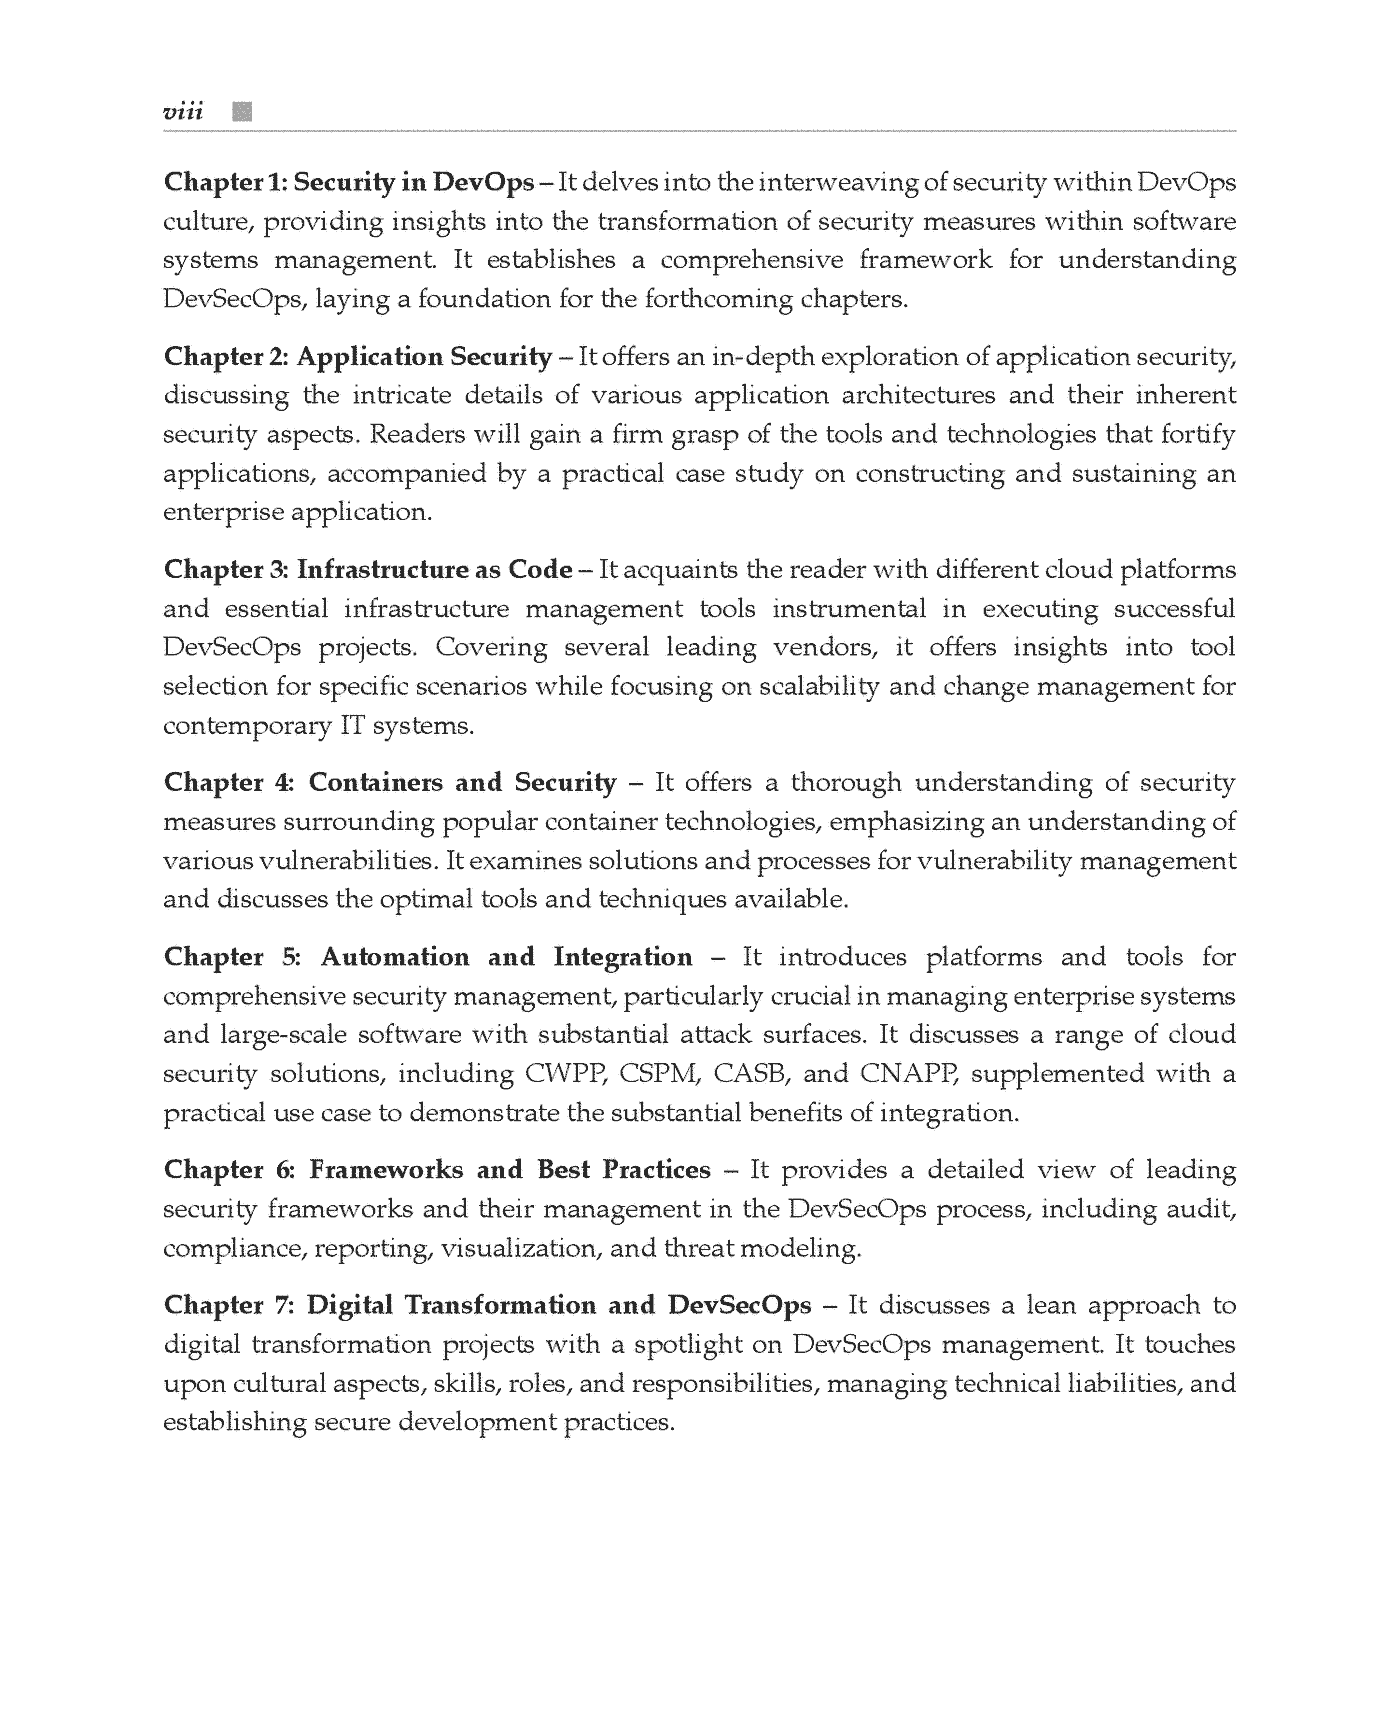
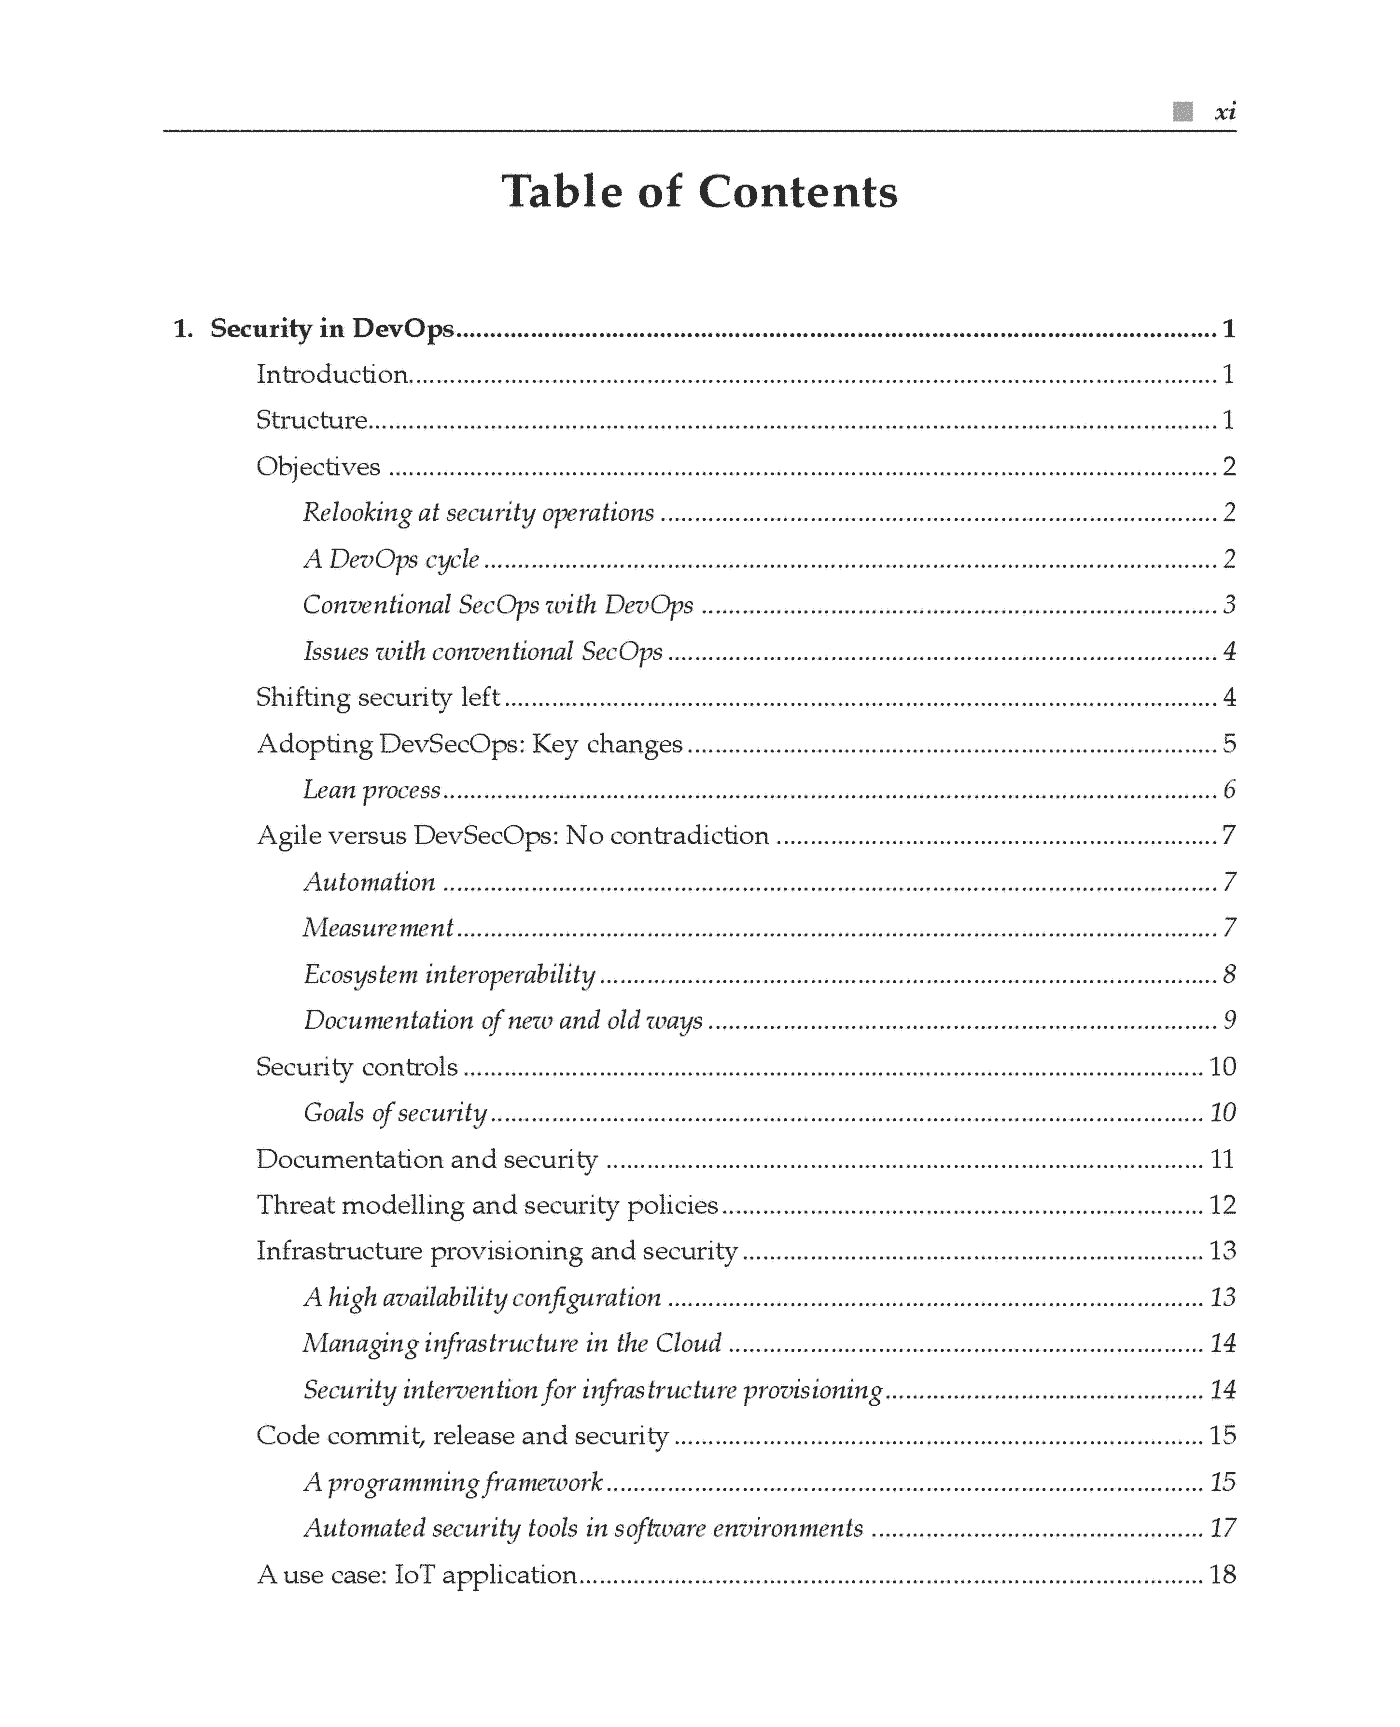
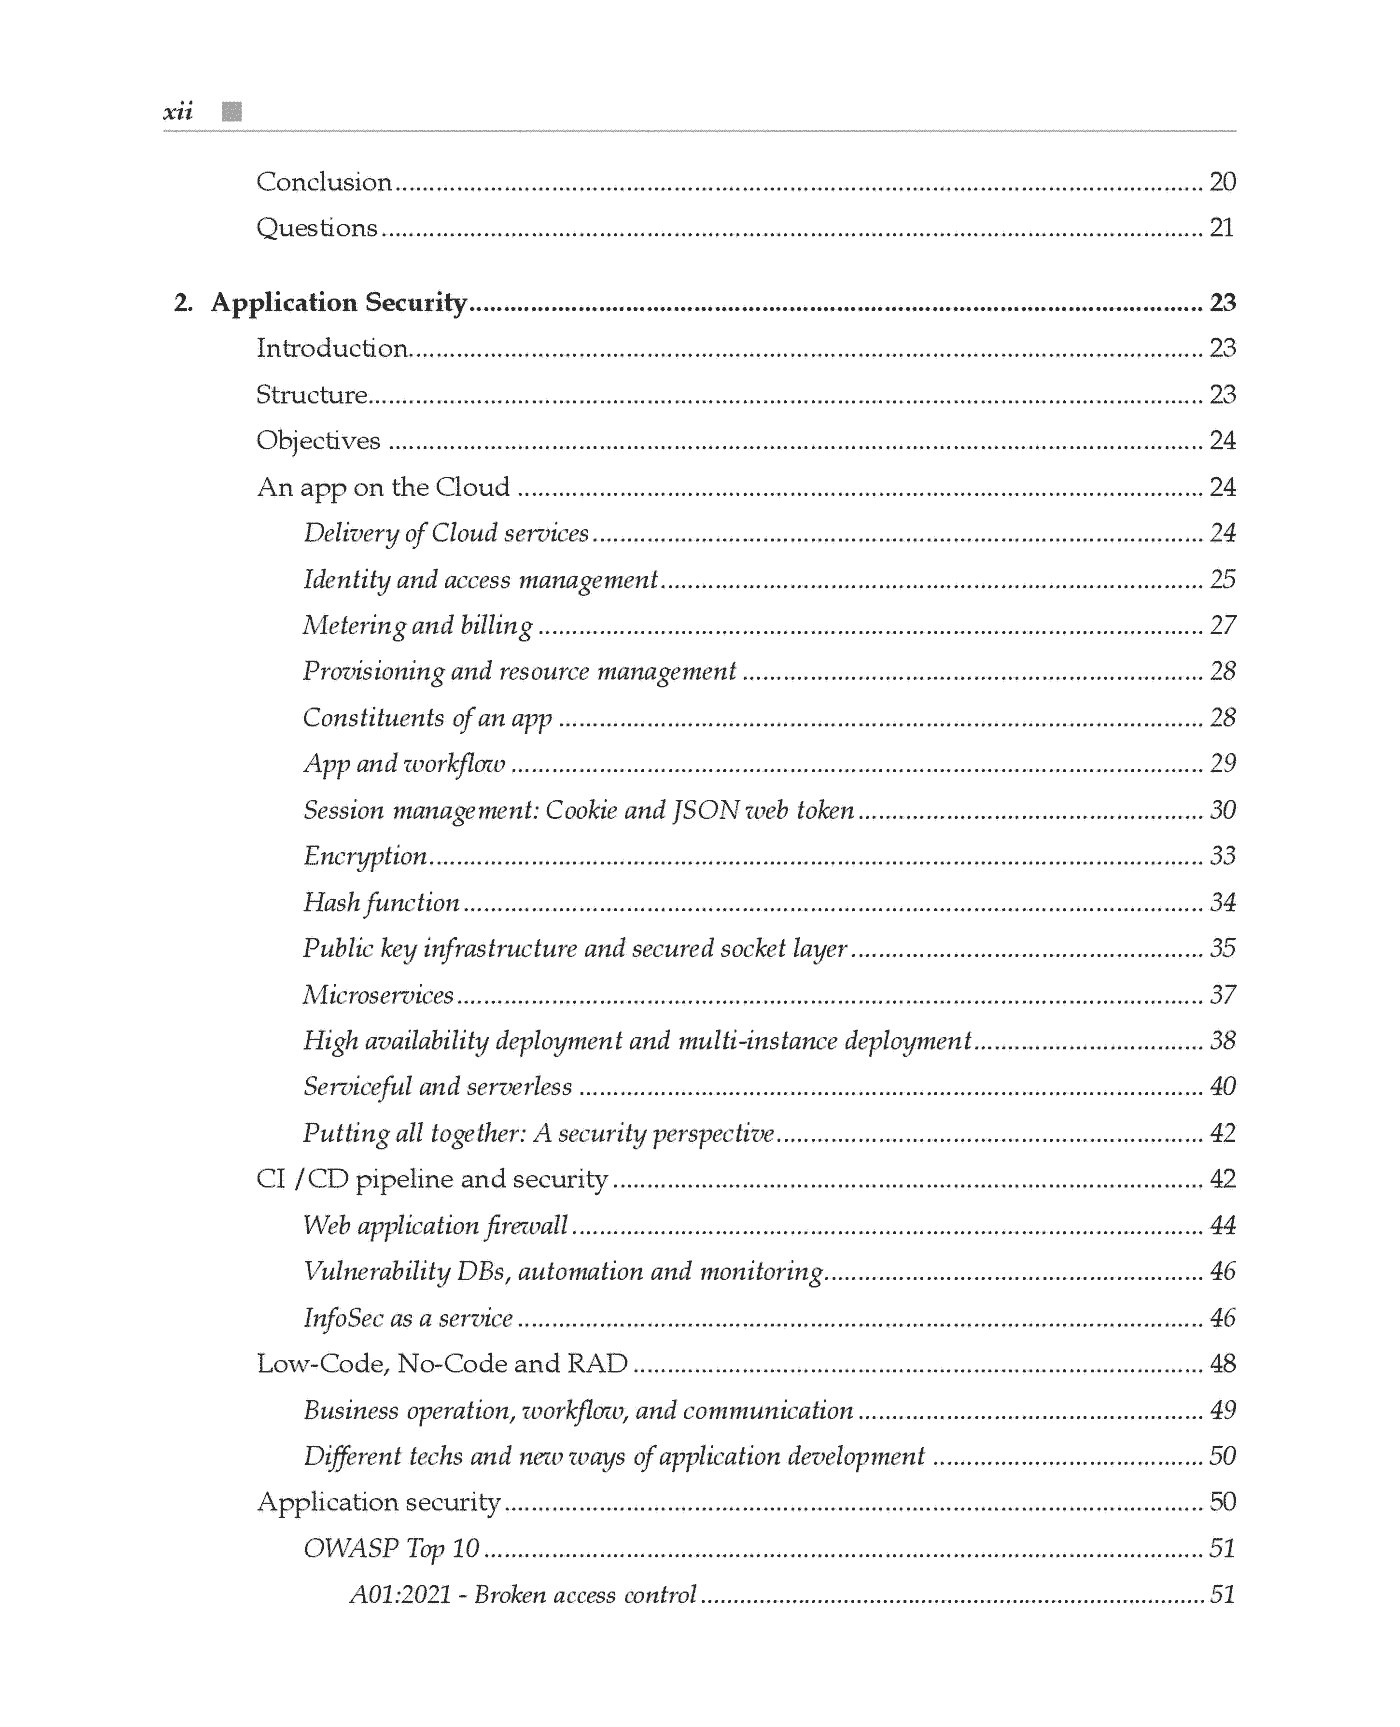
1. Security in DevOps
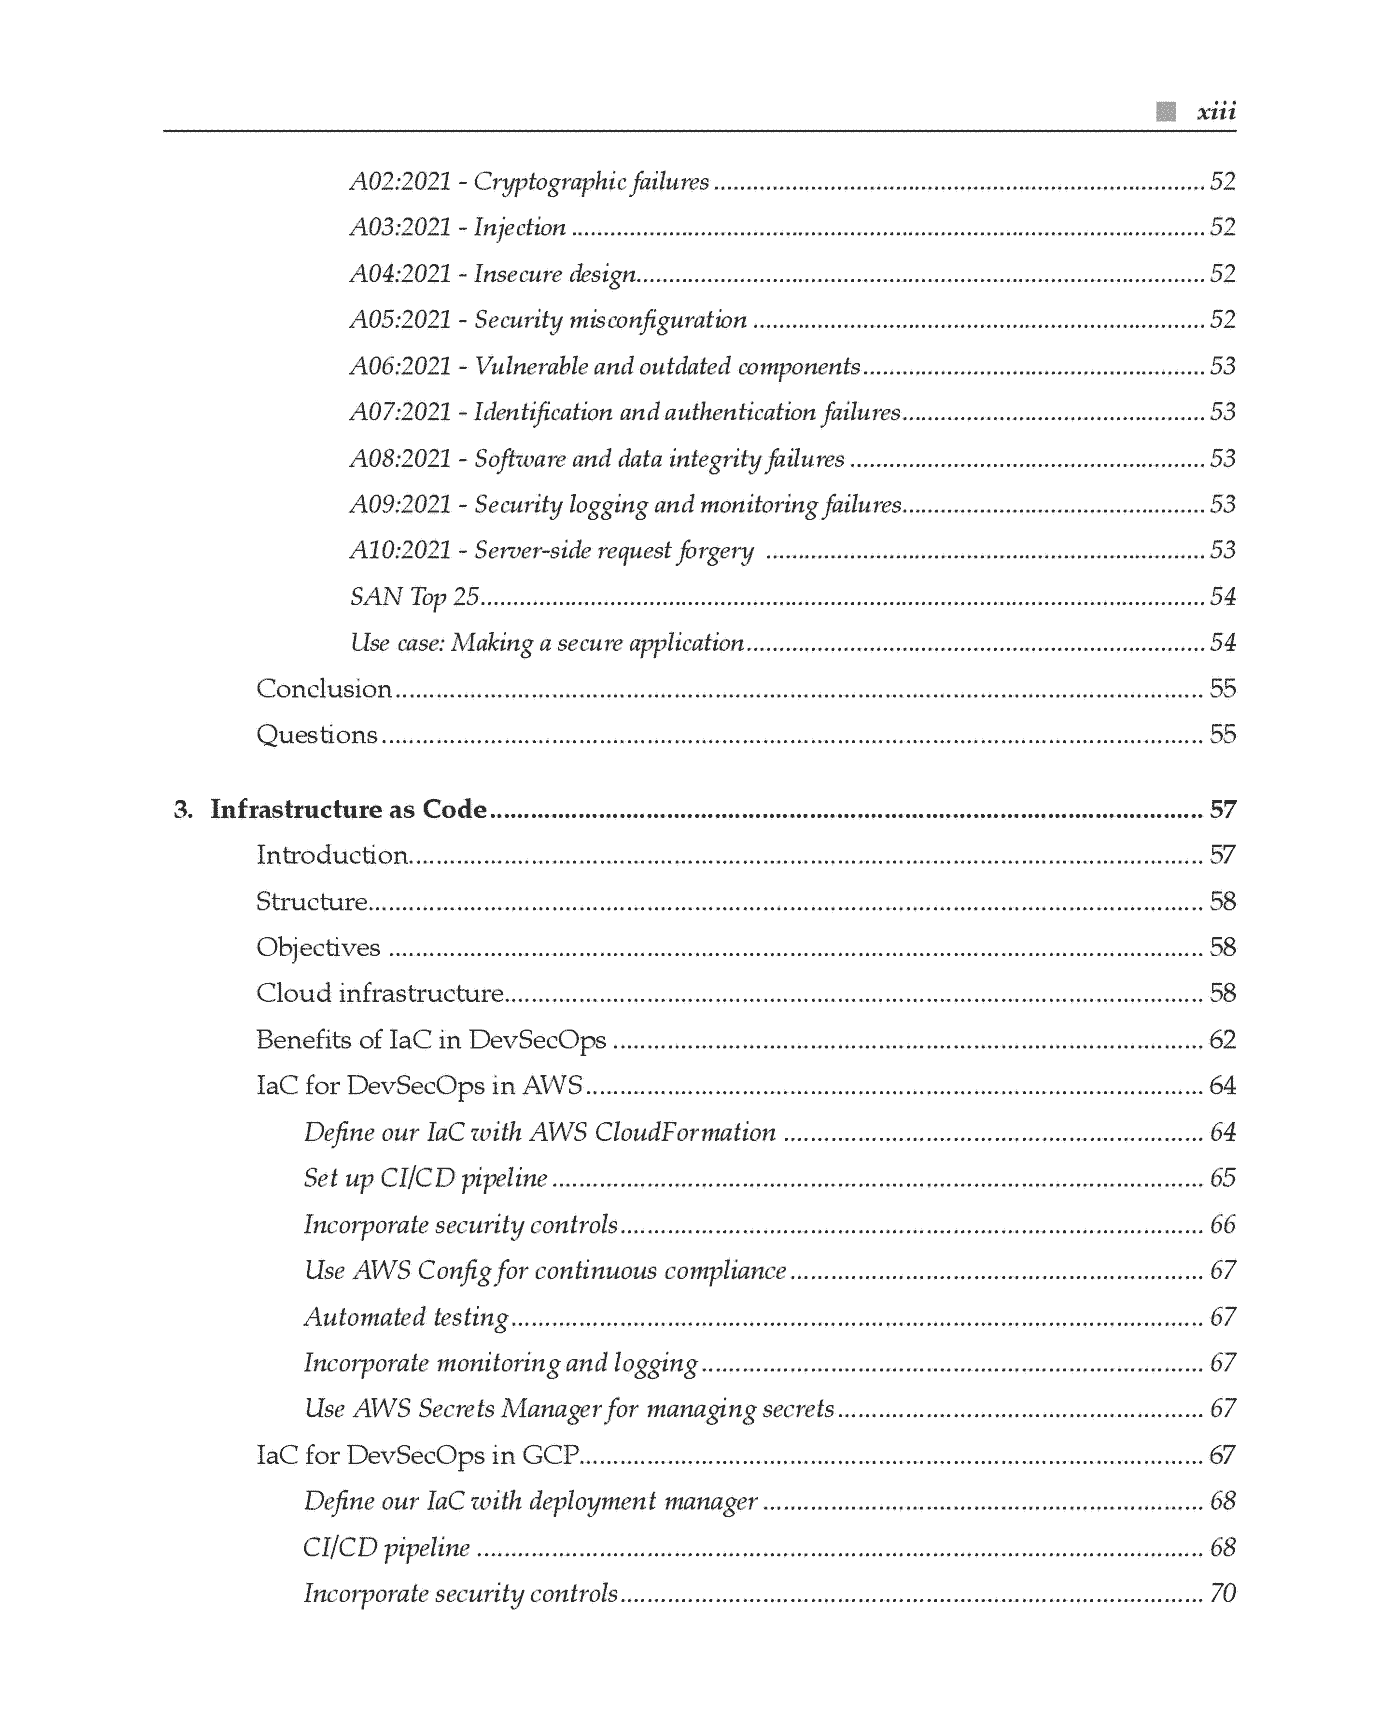
2. Application Security
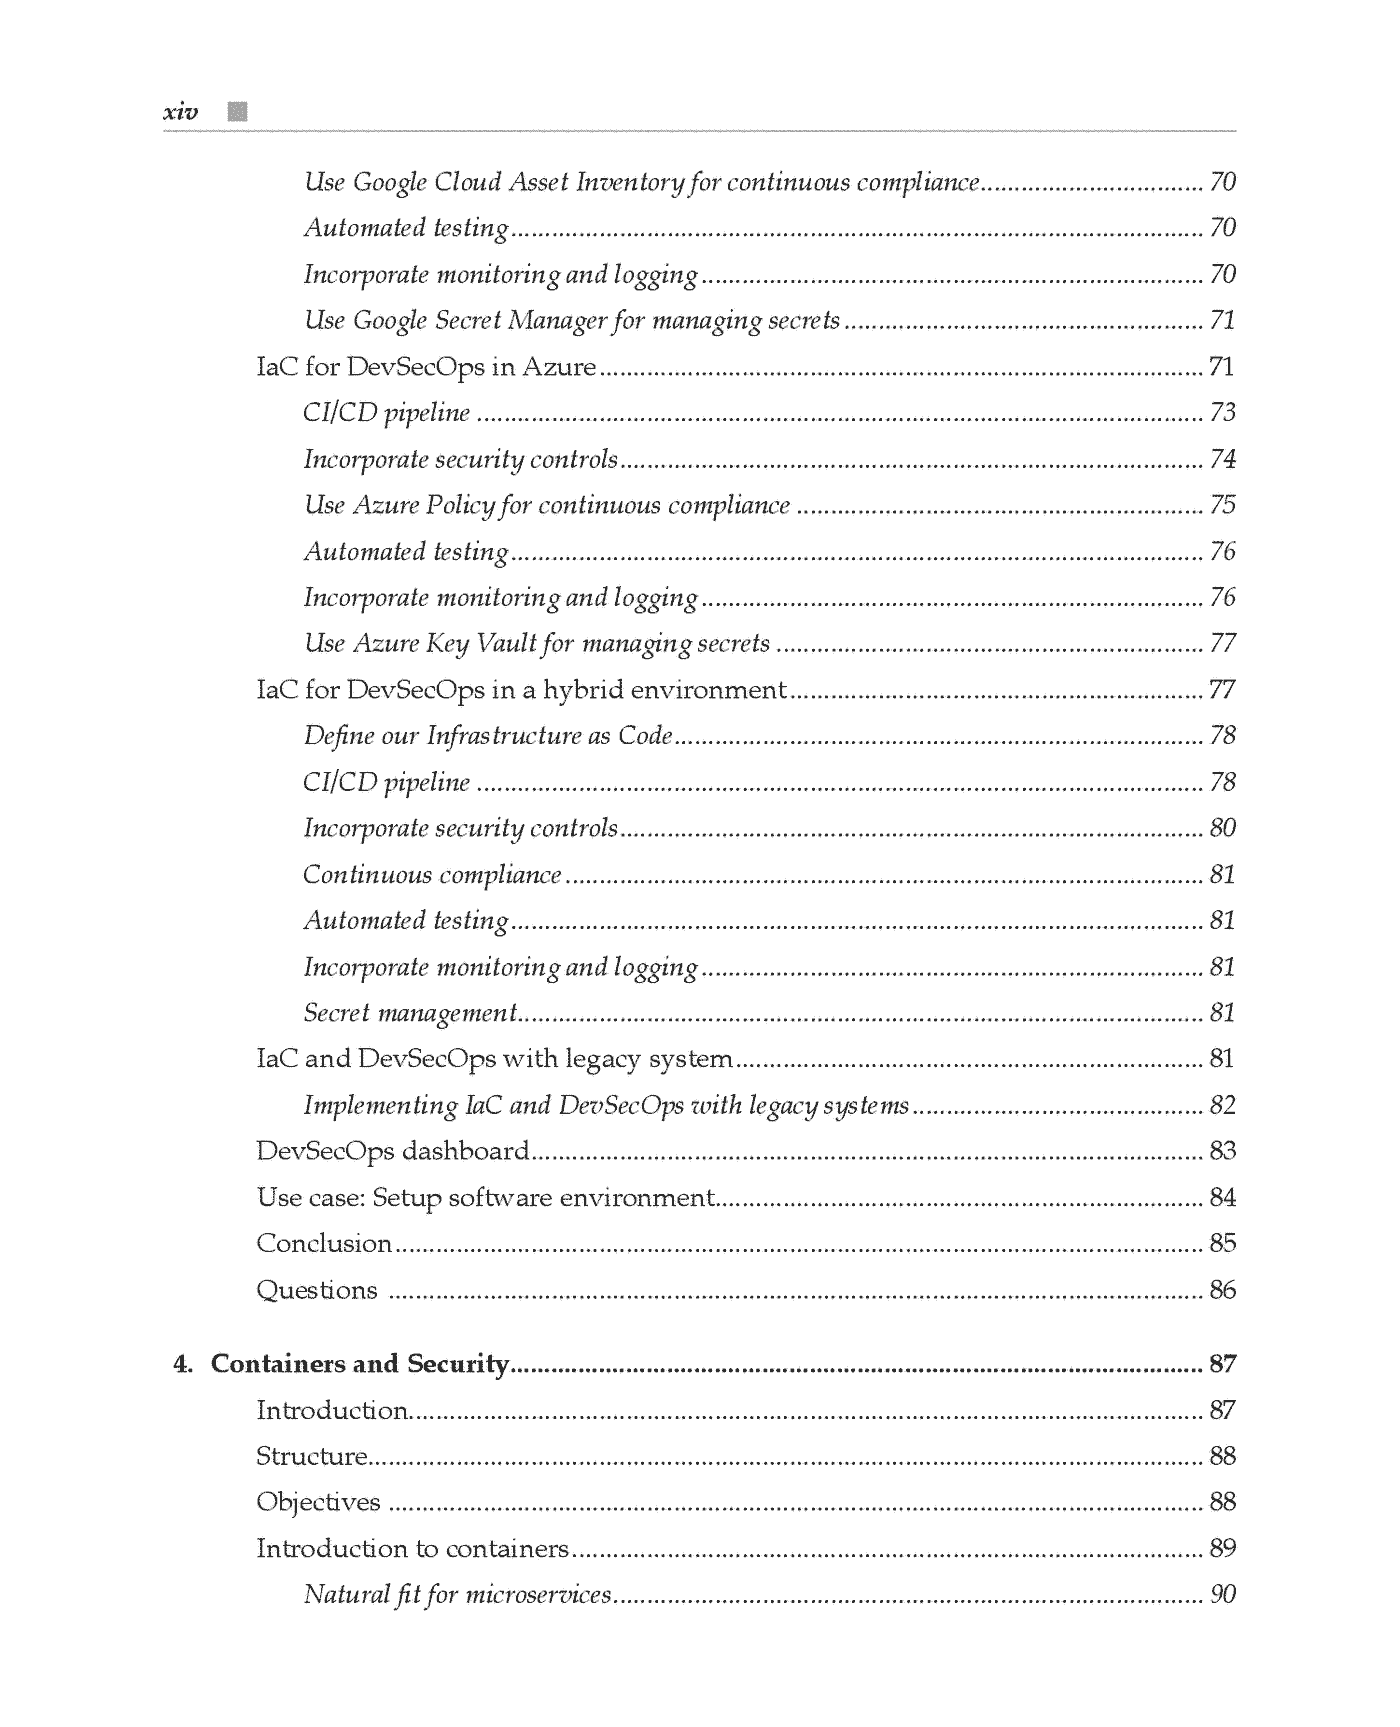
3. Infrastructure as Code
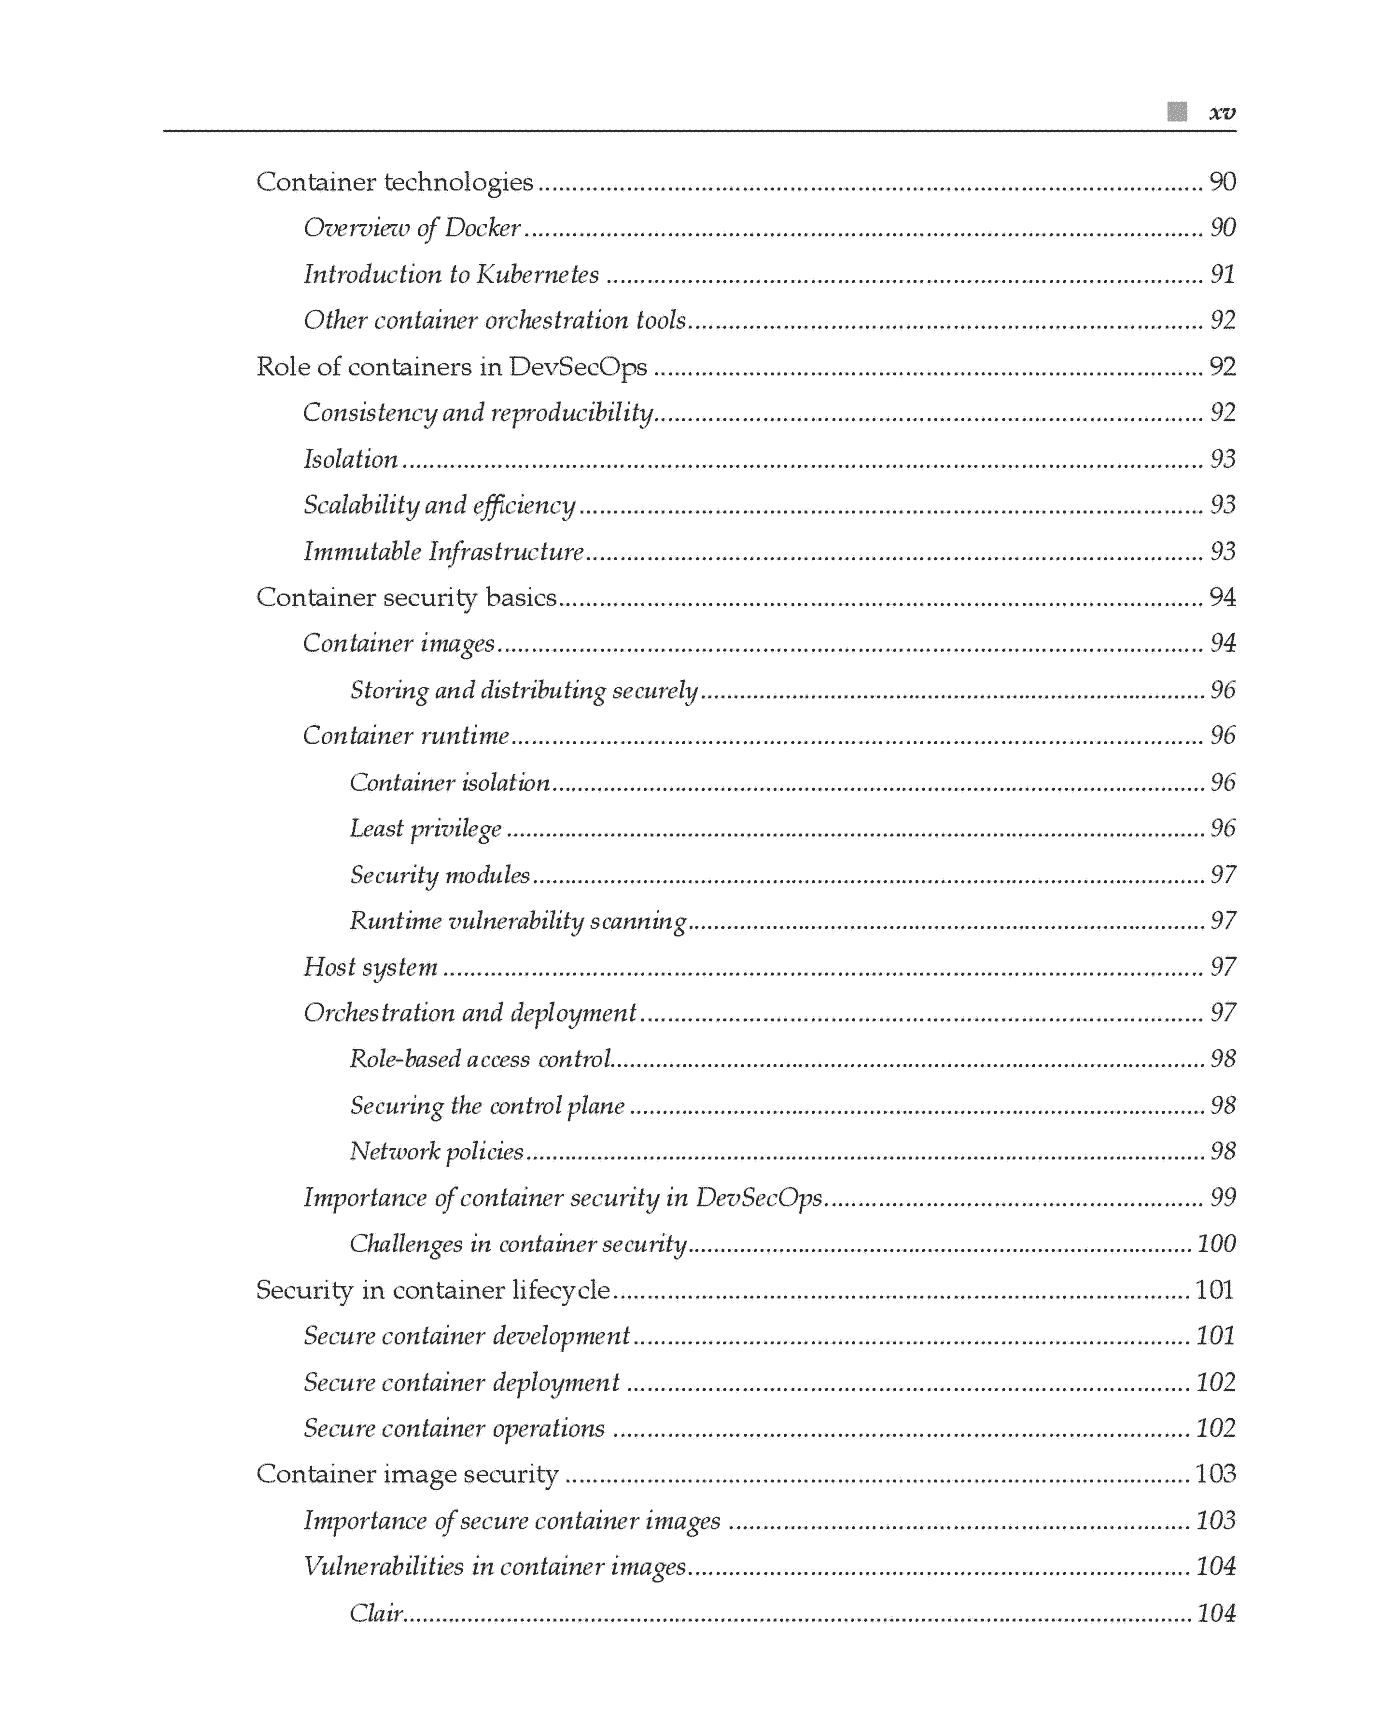
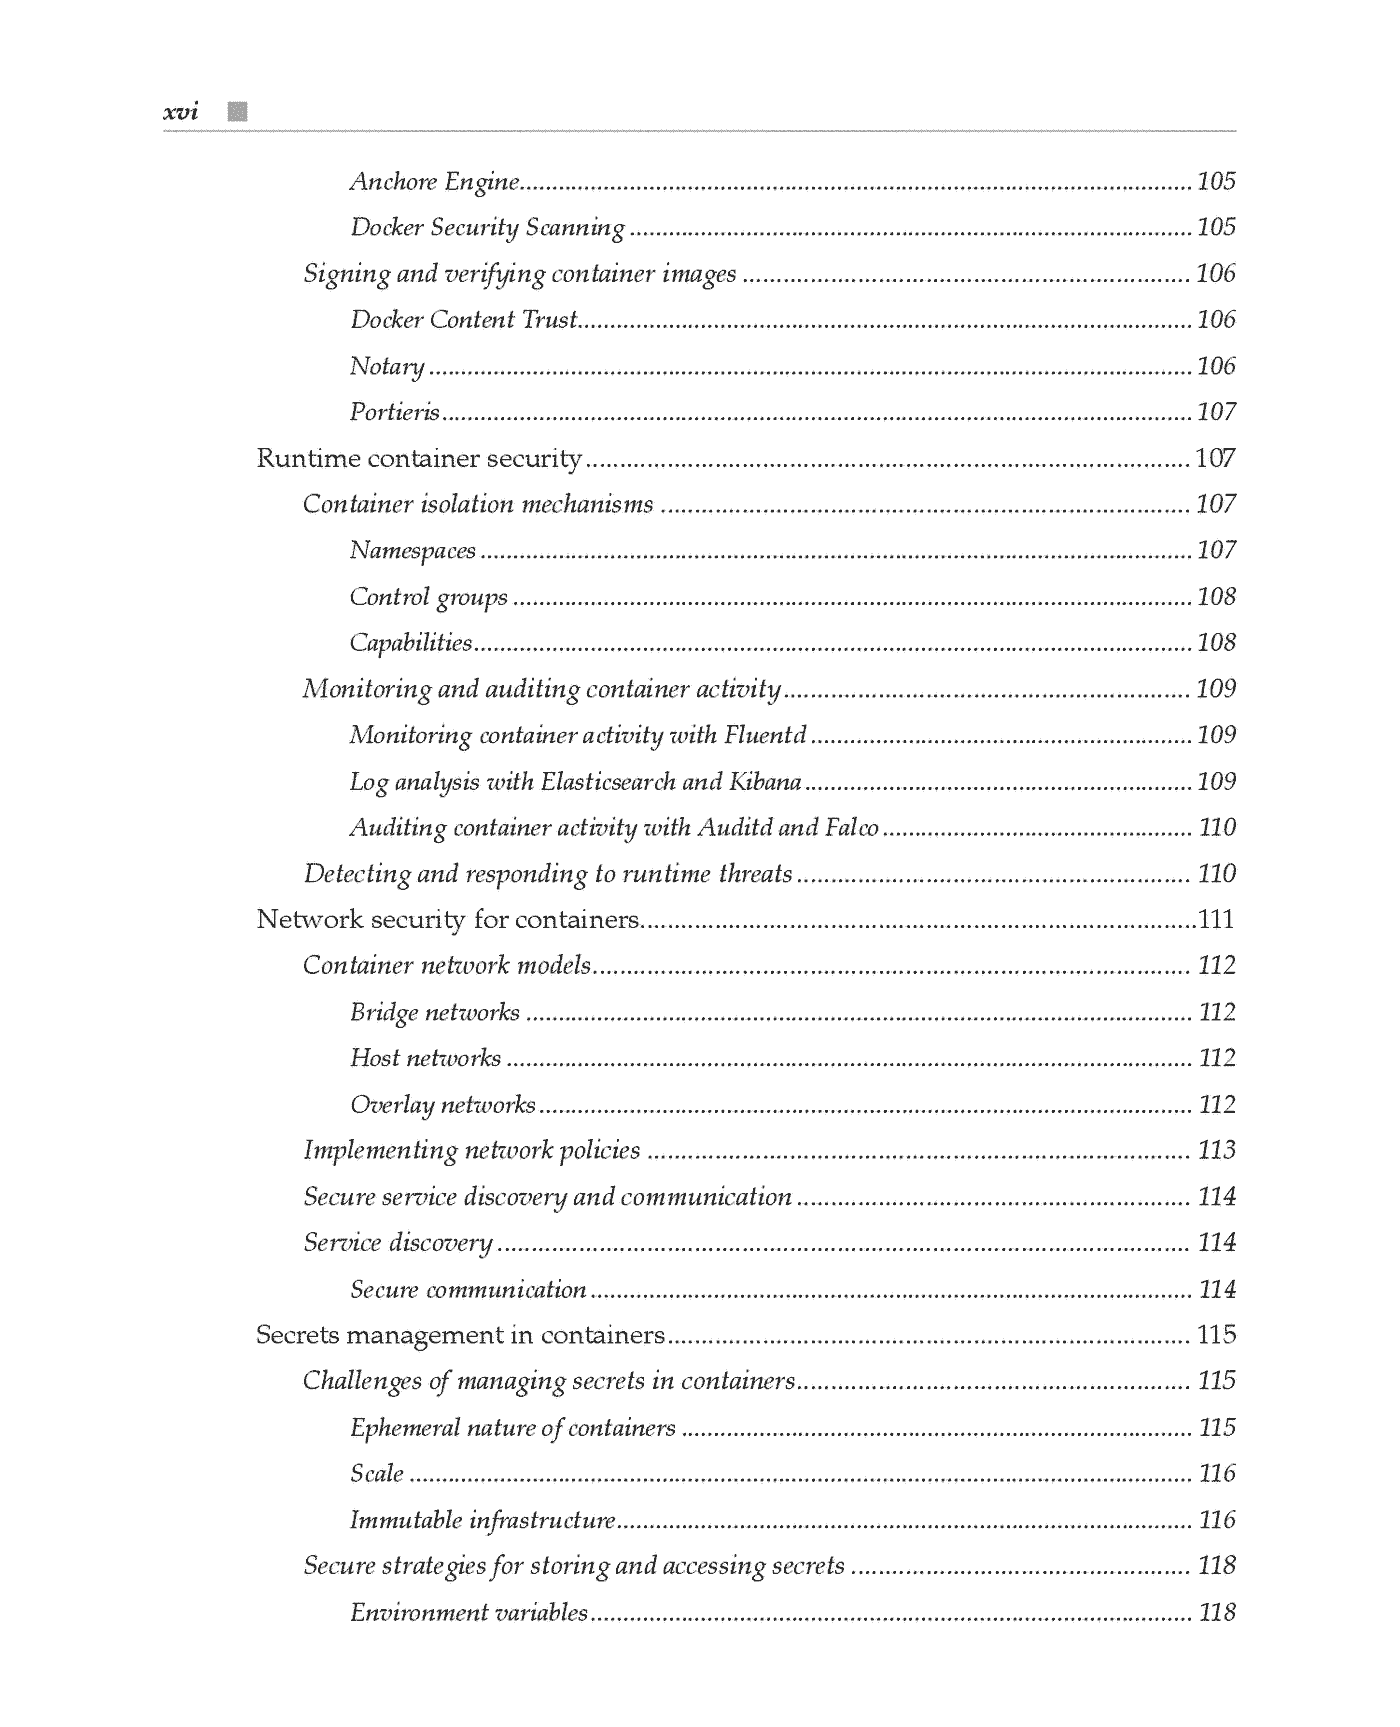
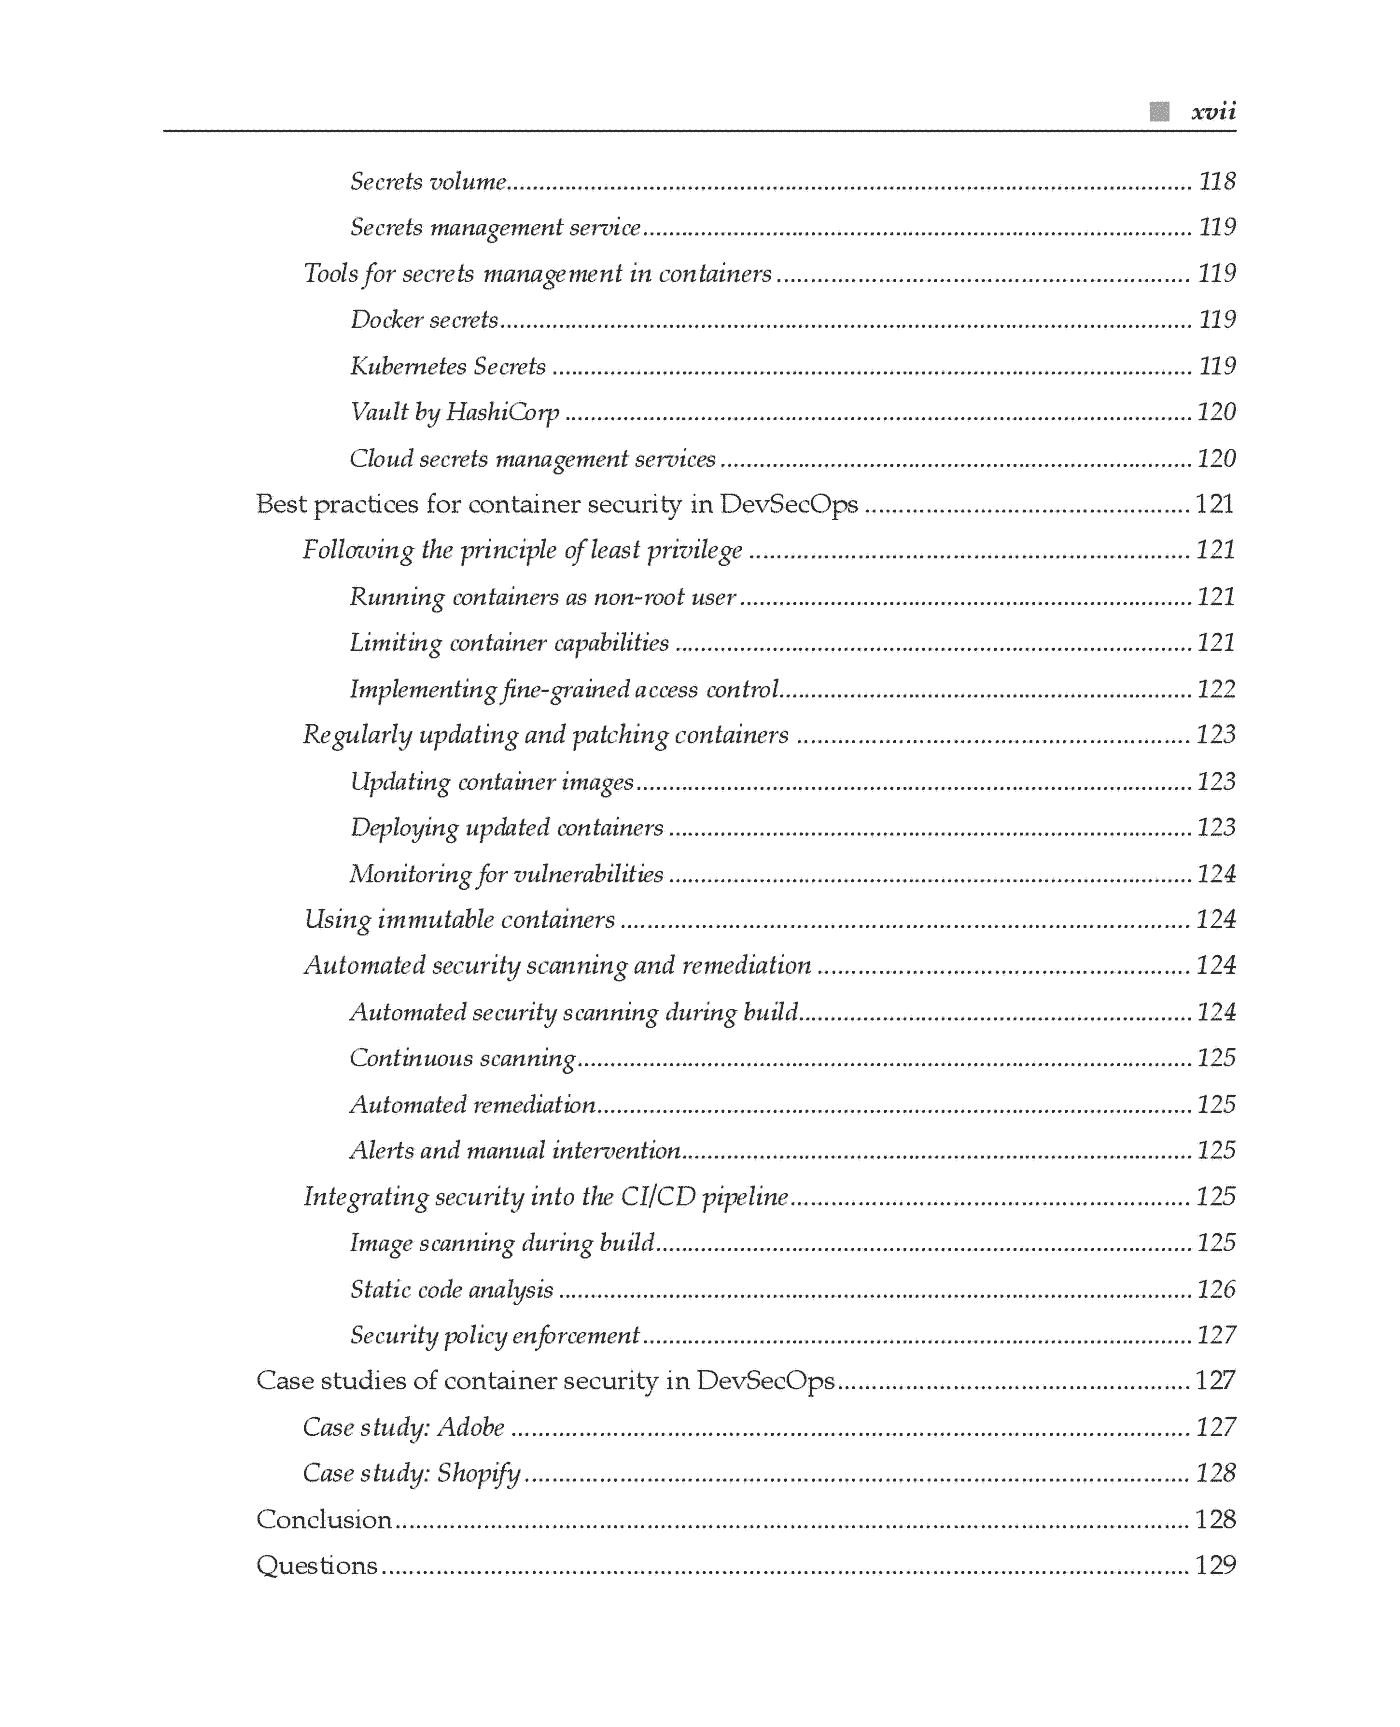
4. Containers and Security
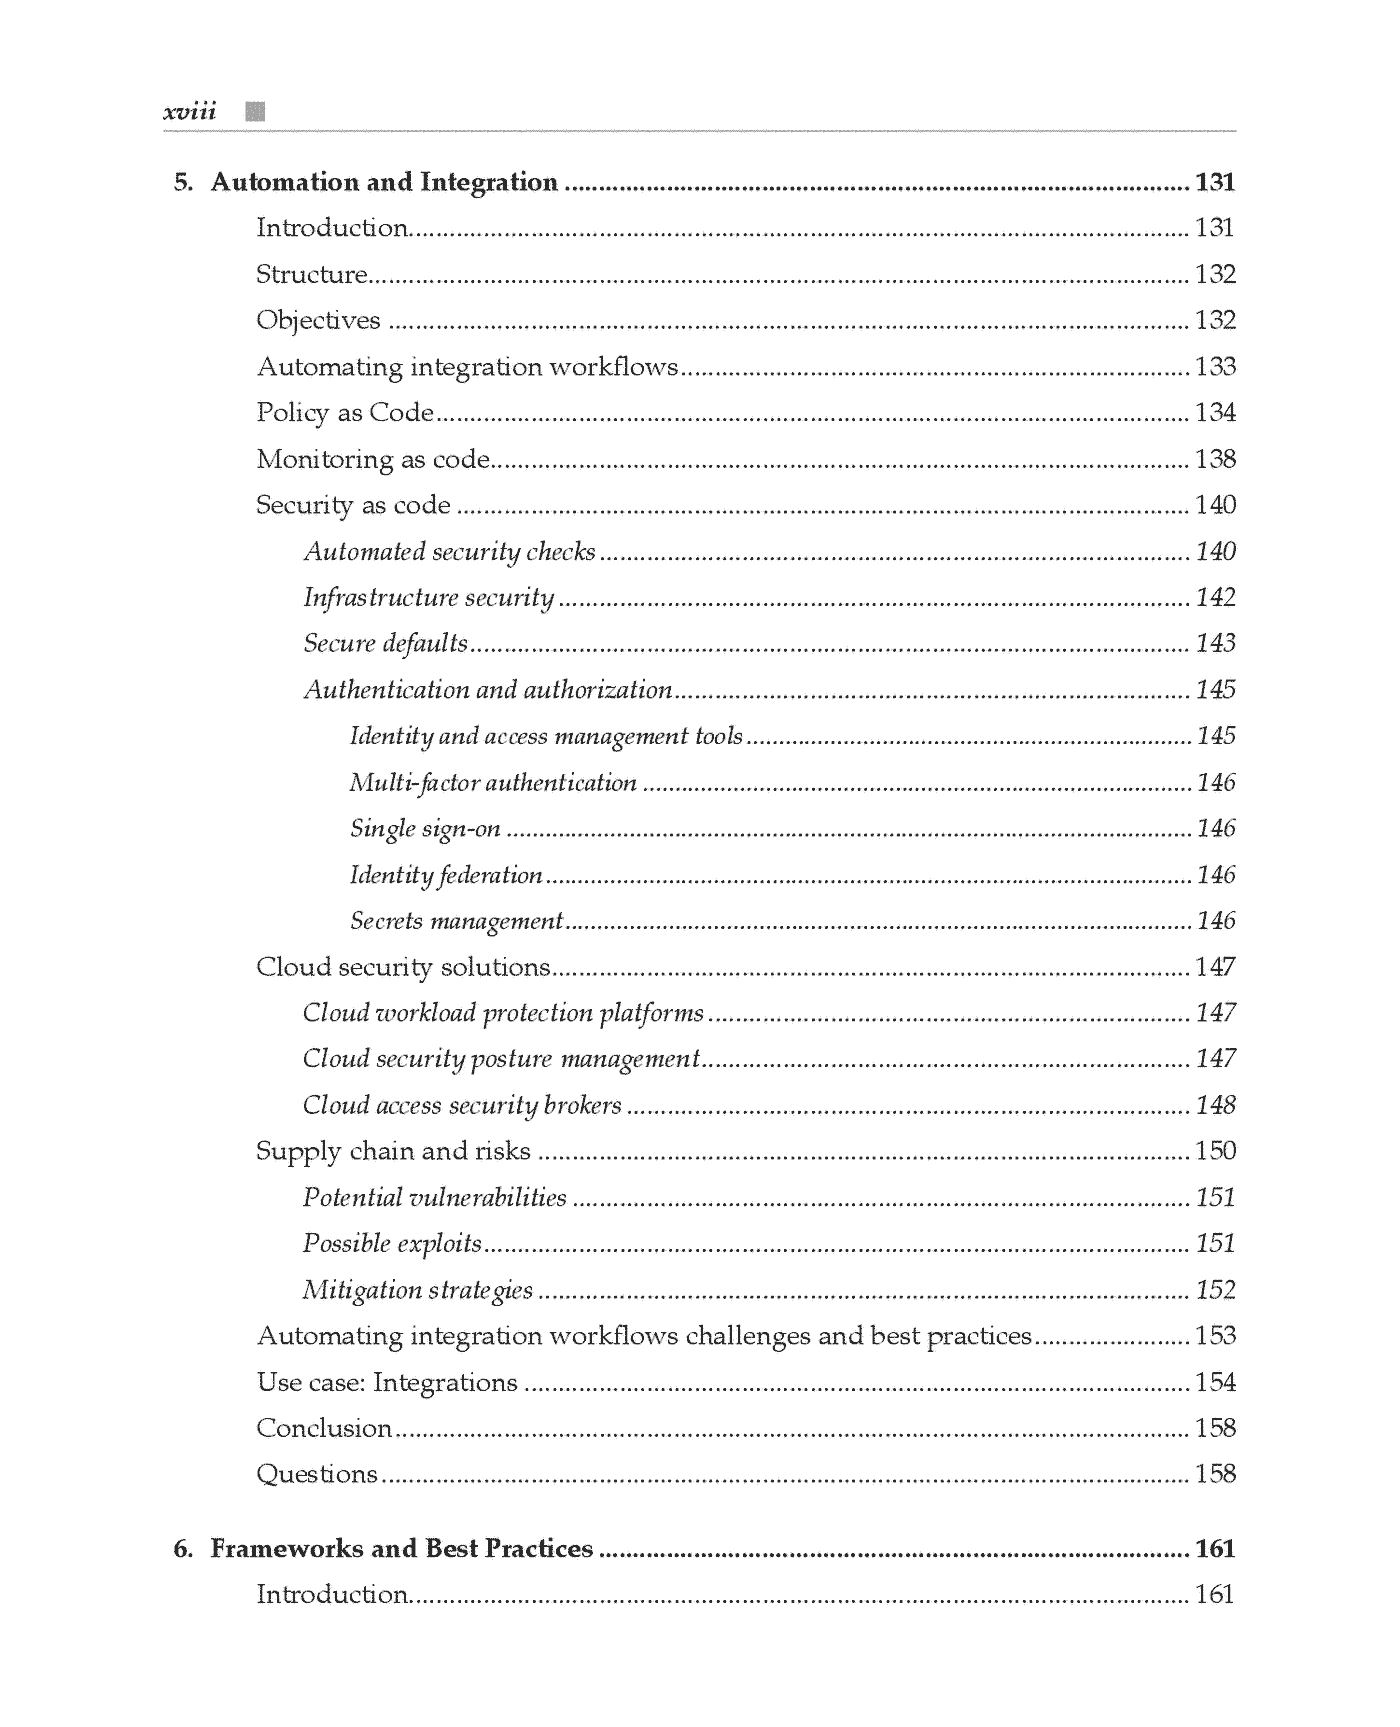
5. Automation and Integration
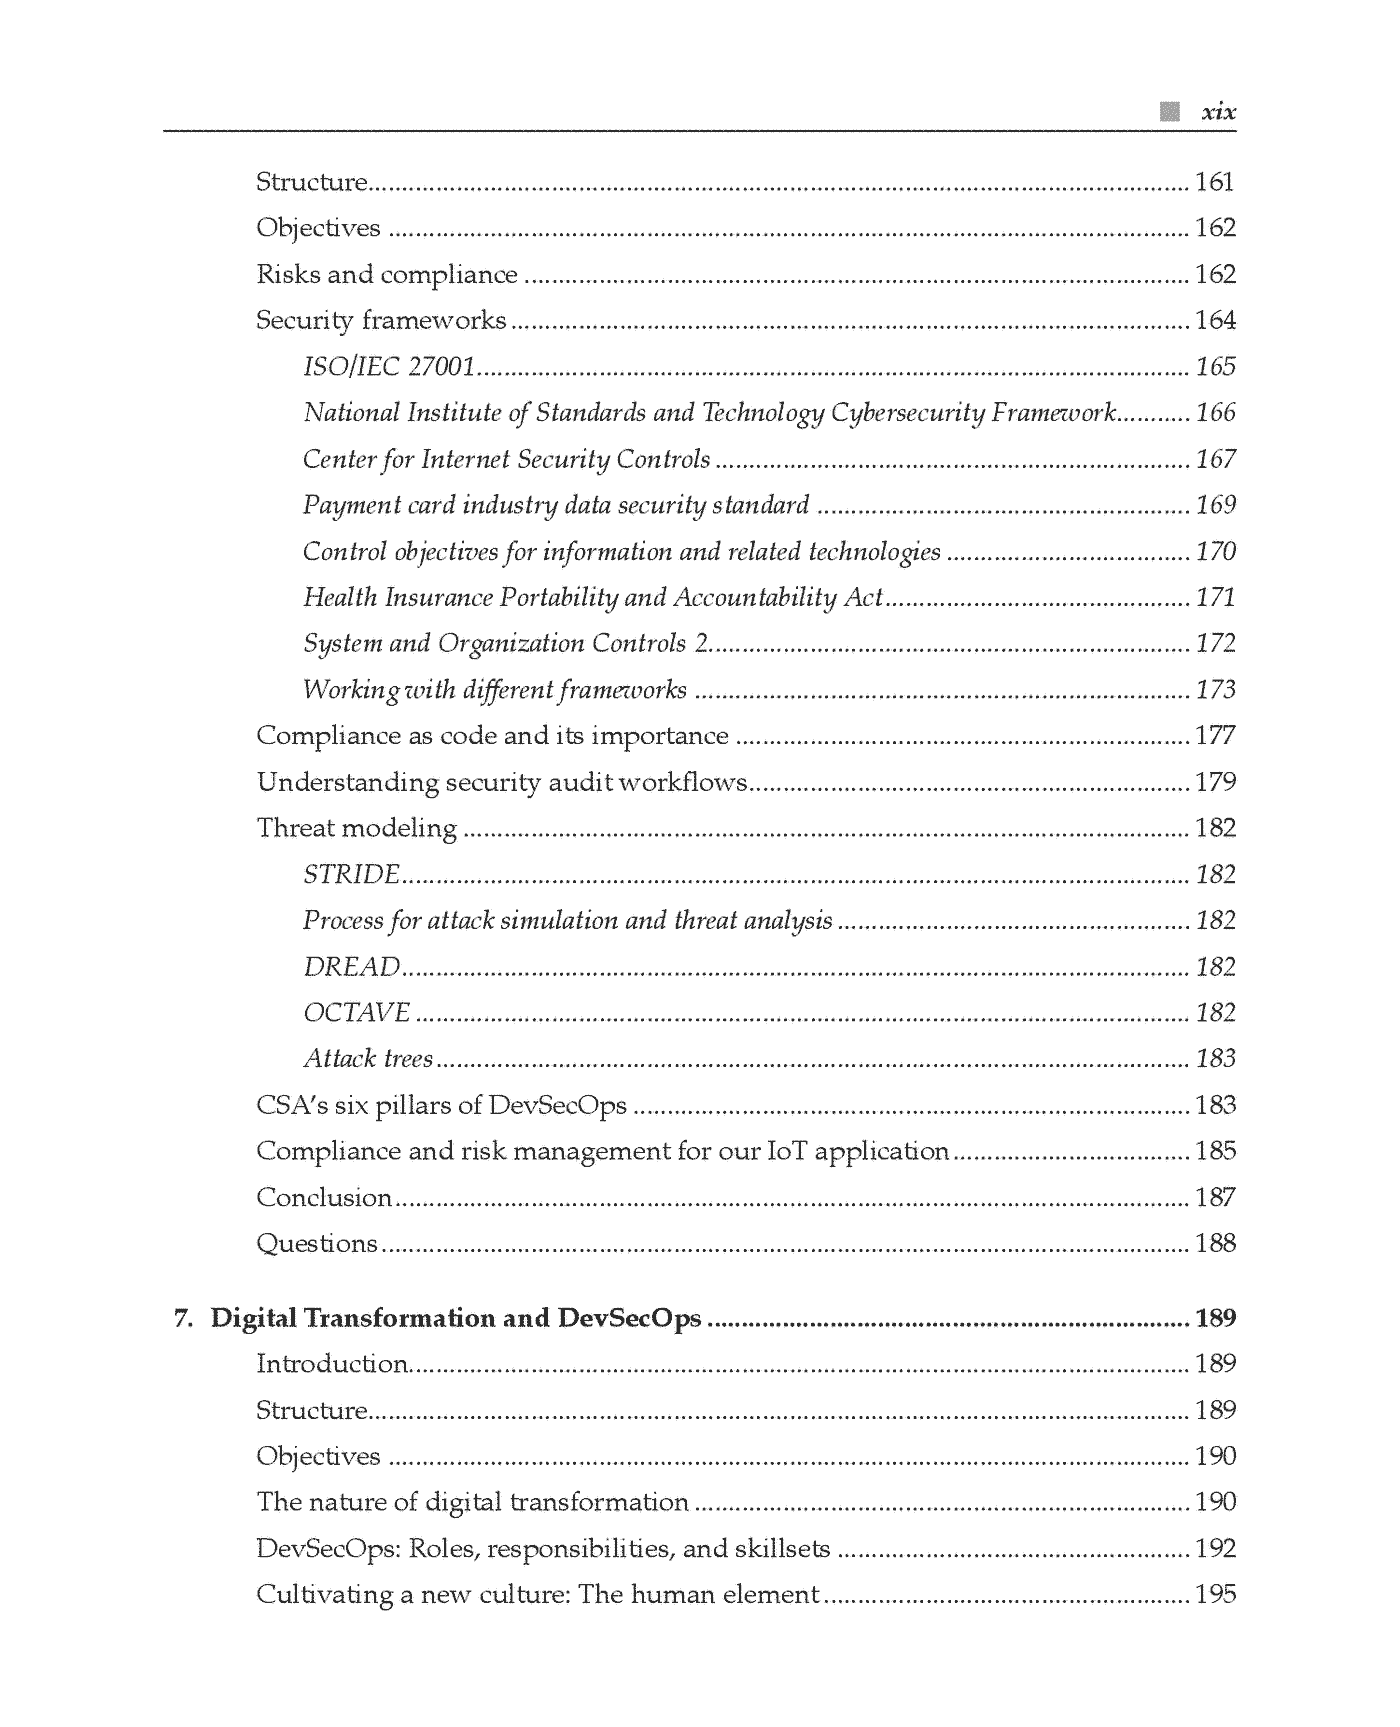
6. Frameworks and Best Practices
7. Digital Transformation and DevSecOps
 1
 2
 3
 4
 5
 6
 7
 8
 9
 10
 11
 12
 13
 14
 15
 16
 17
 18
 19
 20
 21
 22
 23